

Manage your cloud firewalls across every connected provider from one place, and let InfraNest warn you before a risky rule goes live. This article is for anyone responsible for keeping servers locked down, even without a networking background.
Overview
- Edit inbound and outbound rules for all your firewalls in a single editor, regardless of provider.
- See at a glance how many servers each firewall is applied to.
- Get flagged automatically when a rule leaves something dangerously exposed, like a database or remote-access port open to the whole internet.
- Attach a firewall to new servers, rename it, or strip it down to zero rules without deleting it.
Edit a firewall
- Go to Firewalls and open one (or open a server and go to its Firewall tab).
- Edit the inbound and outbound rules — direction, protocol, port, and the source or target IP ranges.
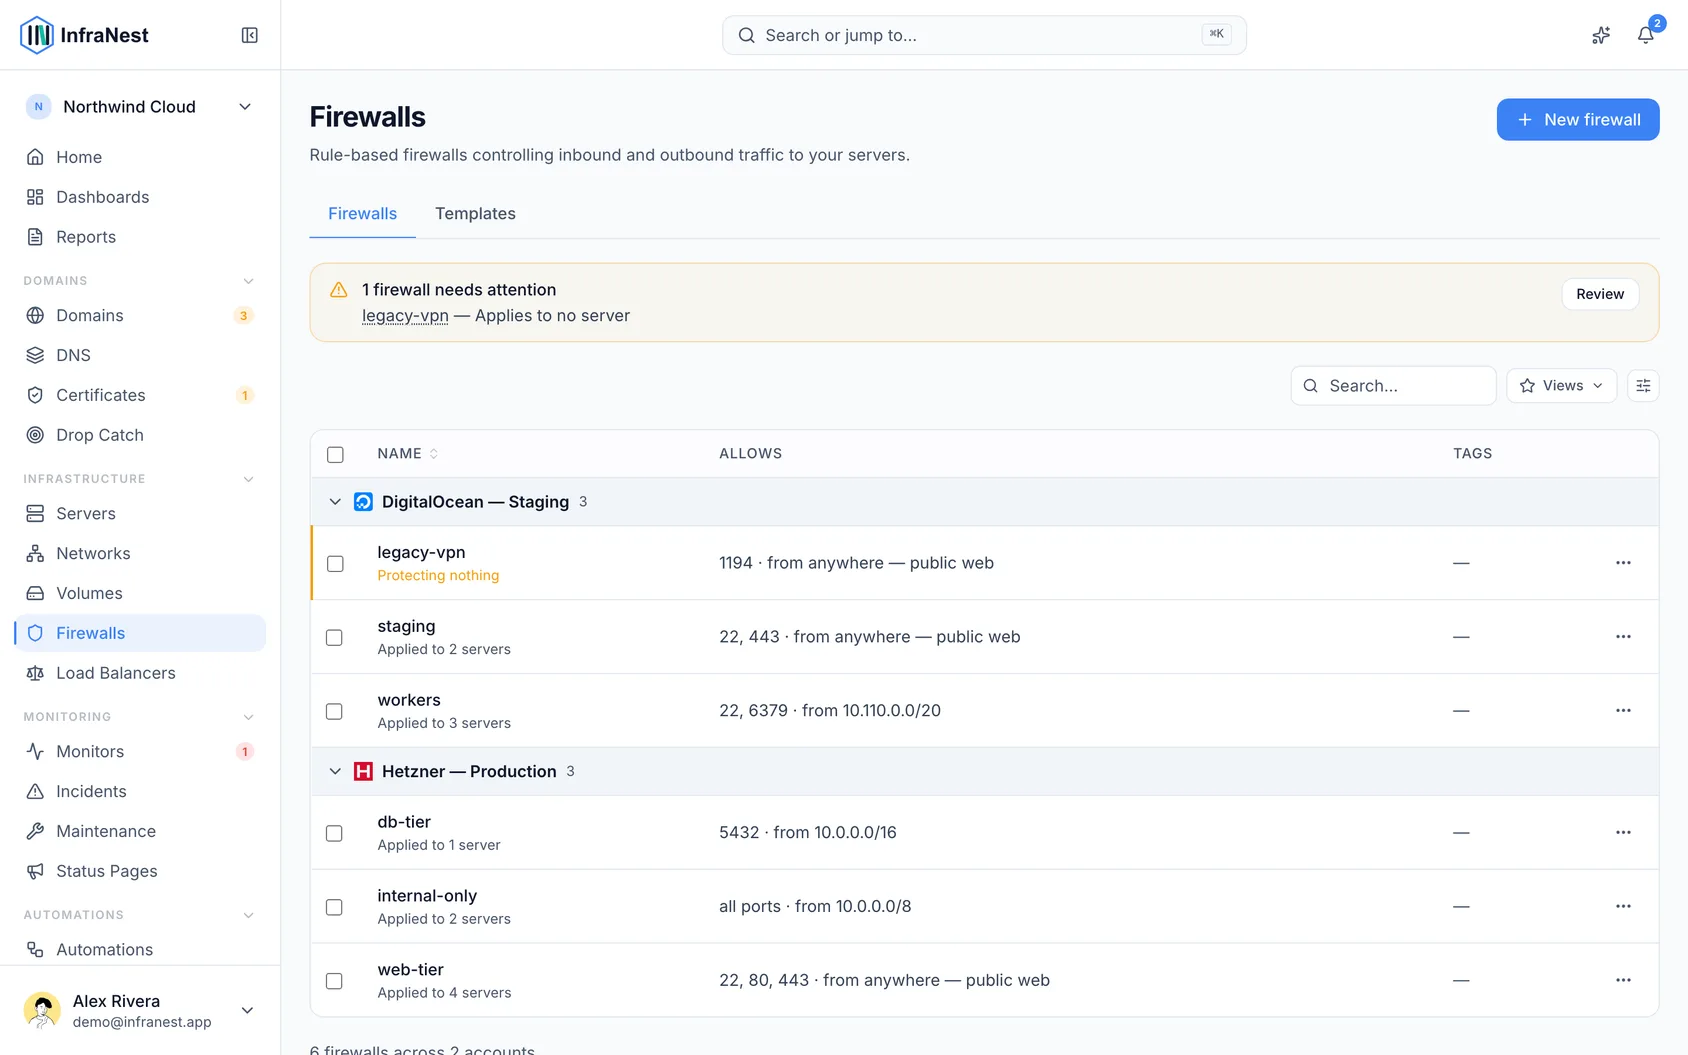
- Select Save. Each firewall shows how many servers it's applied to.
From a server you can also enable, disable, reset or edit the firewall applied to it.
Remove every rule
A firewall with no rules at all is allowed, and it means exactly what it says: nothing gets in.
- Delete the rules you don't want and select Apply.
- The confirmation lists every rule being removed, and warns you first if one of them is what lets you reach the server over SSH or remote desktop.
This is not the same as deleting the firewall. The firewall stays, stays attached to the servers it protects, and simply stops permitting anything — which is what you want if you're locking a server down while you sort something out.
On DigitalOcean, rules written against tags rather than IP addresses aren't ours to remove, so they stay. They're listed separately in the editor, and the firewall still enforces them.
Rename a firewall
- Click the firewall's name at the top of its page.
- Type the new name.
- Press Enter.
The name changes at your provider too, so it stays the same everywhere.
TransIP firewalls can't be renamed — each one belongs to a single VPS and carries that server's name.
Protect another server with a firewall you already have
- Open the firewall and select Attach a server in the Applied to panel — or open the server and select Attach on its Attached card.
- Pick the server (or the firewall, from the server side) and confirm. It starts protecting straight away.
- To stop protecting a server, select the ✕ next to it in the Applied to list.
You can only combine a firewall and a server from the same provider account, so anything you can pick will work.
The Firewall Advisor
As you review a firewall, InfraNest flags risky exposure — like SSH open to the whole internet, remote desktop open to the world, or a database port exposed publicly — with an explanation and a fix, so dangerous rules are caught before they cause trouble.
TipA firewall rule can follow a changing IP automatically — see Set up Dynamic IP.
Addresses we can't account for
When a Dynamic IP keeps part of a firewall up to date, we also look at what else that rule allows — and tell you about anything we didn't put there.
You'll see one of two things:
- An address we used to keep up to date, named, with the date we stopped. This is the one worth acting on: it was yours under an old internet connection, it isn't maintained any more, and providers hand old addresses to other customers.
- An address we didn't write. Nothing is wrong with it as far as we know — it may be a colleague, an office, or a monitoring service — we simply can't tell you what it is.
Nothing is ever removed for you. An allow-entry we didn't write isn't ours to delete, so we show it and leave the decision with you; edit the rule yourself if it should go.
Say what it is. Use Say what this is to write a short note — "Berlin office", "Pingdom probe". The entry stops being a question, and the next person to look (including you in six months) doesn't have to work it out again. Clearing the note marks it unexplained again.
You'll be emailed once about an address we used to maintain, because that one we can be sure about. We don't email about addresses we simply don't recognise — you'd hear about every entry you already know about, on the first check.
Rules that nothing tracks are left alone, and a rule where your Dynamic IP is the only address stays quiet.
What a firewall rule does and does not cover
When a rule is open to the whole internet, the fix is to restrict its source to the addresses that need to reach that port — your own IP, your office range, or the address of the server that calls it. Select Limit to My IP on the warning to do that in one step.
A private network is not a narrower source to put in that box.
WarningOn some providers — Hetzner among them — firewall rules only cover traffic that arrives on the server's public address. Anything sent over a private network reaches the server without being checked against any rule you write here, so a rule whose source is a private range like
10.0.0.0/24matches nothing and blocks nothing. Where that is the case, the editor says so above the inbound rules.
That does not make a private network unsafe — it means a different thing controls it. There, who is attached to the network decides who can reach the server, and you manage that on the network itself rather than with rules. See Private networks for what attaching a server grants.
Tips
- Save a good rule set as a firewall template so you can apply the same protection across many servers at once.
Was this article helpful?